Your Digital Future.Our Cybersecurity Commitment.
Talk To Us
The United Kingdom s digital economy depends on secure infrastructure, trusted identities, resilient applications, protected data, and reliable technology services.
Cyber threats are becoming more complex. Ransomware, phishing, business email compromise, identity attacks, cloud misconfigurations, supply chain vulnerabilities, and AI-enabled threats can affect businesses of every size.
CyberSec Consulting helps UK organisations strengthen their security posture through cybersecurity consulting, security assessments, managed security services, identity security, cloud security, GRC consulting, data protection, penetration testing, SOC consulting, and cybersecurity implementation services.
Our services support businesses across England, Scotland, Wales, and Northern Ireland. We help organisations identify security gaps, improve cyber resilience, protect critical assets, meet regulatory expectations, and support secure digital growth.
CyberSec Consulting works with enterprises, public sector organisations, financial institutions, healthcare providers, technology companies, manufacturers, retailers, professional services firms, and critical infrastructure operators.
Why Cybersecurity Matters for UK Organisations
The UK business environment relies on interconnected digital systems, cloud platforms, remote access, online services, APIs, third-party suppliers, and sensitive information.
Cybersecurity Challenges Facing UK Businesses
Ransomware and Extortion
Ransomware can interrupt business operations, encrypt critical systems, expose confidential information, and create serious recovery costs.
- Endpoints
- Servers
- Cloud workloads
- Identity systems
- Privileged accounts
- Backup infrastructure
- Network devices
- Business applications
- Security monitoring platforms
Third Party and Supply Chain Risk
UK businesses often depend on technology providers, managed service providers, software suppliers, contractors, and digital platforms. A weakness within a supplier environment can affect multiple connected organisations.
- Supplier security controls
- Access permissions
- Data-sharing arrangements
- Security responsibilities
- Cloud dependencies
- Vendor risk
- Incident notification processes
- Business continuity arrangements
Cloud Security Misconfigurations
UK organisations are increasingly dependent on cloud infrastructure and cloud-based applications. Misconfigured storage, excessive permissions, exposed services, insecure APIs, weak authentication, and poor monitoring can increase business risk.
- Cloud security assessment
- Cloud configuration reviews
- Cloud IAM consulting
- Cloud workload protection
- Cloud security architecture
- Cloud compliance assessments
- CSPM consulting
- Cloud risk management
Business Email Compromise
Business Email Compromise can target finance teams, senior executives, suppliers, and procurement processes. Attackers may impersonate executives, alter payment instructions, compromise mailboxes, or manipulate business communication.
- Email security
- Identity protection
- MFA
- Privileged access controls
- User awareness
- Threat detection
- Payment process verification
- Incident response
Data Protection and Privacy Risks
UK organisations process customer, employee, financial, healthcare, operational, and commercially sensitive information. Data protection requires visibility into how information is collected, stored, accessed, transferred, retained, and deleted.
- Data classification
- Data discovery
- Data security assessments
- Data Loss Prevention
- Privacy assessments
- Information governance
- Access governance
- Sensitive data protection
- Data protection compliance
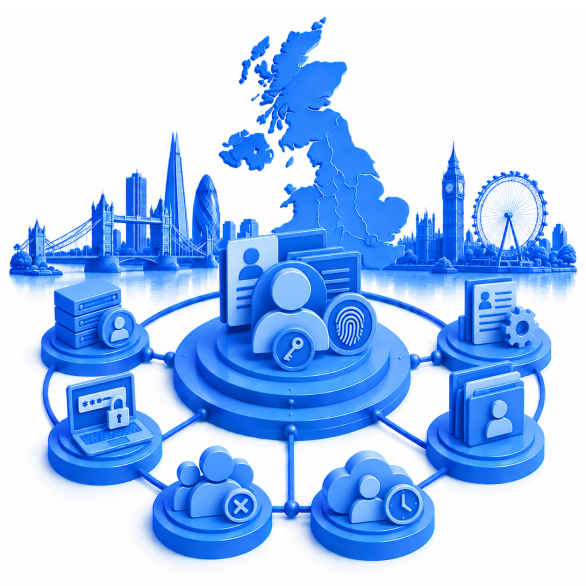
Identity-Based Attacks
Identity has become a critical security boundary for UK businesses. Compromised credentials, excessive permissions, dormant accounts, weak authentication, privileged access abuse, and poor identity lifecycle management can create direct pathways into sensitive systems.
- Identity and Access Management
- Privileged Access Management
- Single Sign-On
- Multi-Factor Authentication
- Identity Governance
- Access Reviews
- Role-Based Access Control
- Joiner-Mover-Leaver processes
- Privileged account monitoring
Cybersecurity Services for UK Organisations
CyberSec Consulting provides a comprehensive portfolio of cybersecurity services in the UK to help organisations manage risk, improve resilience, and protect critical business assets.
Cybersecurity Assessment Services in the UK
A cybersecurity assessment helps organisations understand whether their security controls are effective against current threats. CyberSec Consulting provides UK-focused security assessments covering technology, processes, identities, applications, data, and operational capabilities.
Cybersecurity Risk Assessment
Identify and prioritise risks affecting business-critical systems, information, applications, and operations.
Vulnerability Assessment
Discover vulnerabilities across networks, endpoints, servers, applications, cloud workloads, and infrastructure
Penetration Testing
Validate whether security weaknesses can be exploited through controlled and authorised testing.
IAM Health Check
Assess identity architecture, access governance, authentication, privileged access, identity lifecycle processes, and access review controls.
PAM Assessment
Review privileged account management, credential protection, session monitoring, service accounts, and administrative access.
Cloud Security Assessment
Identify misconfigurations, excessive permissions, exposed resources, insecure workloads, and cloud governance gaps.
Web and Mobile Application Testing
Assess applications for security weaknesses affecting authentication, authorisation, sessions, APIs, data, and business logic.
Security Maturity Assessment
Measure the maturity of security governance, operational controls, incident response, monitoring, risk management, and resilience.
Third Party Risk Assessment
Evaluate supplier security practices, data access, technology dependencies, and external exposure.